Databricks Releases On-Behalf-Of-User Authorization
Databricks has made on-behalf-of-user authorization generally available, enabling developers to build AI apps that automatically respect existing Unity Catalog data permissions.
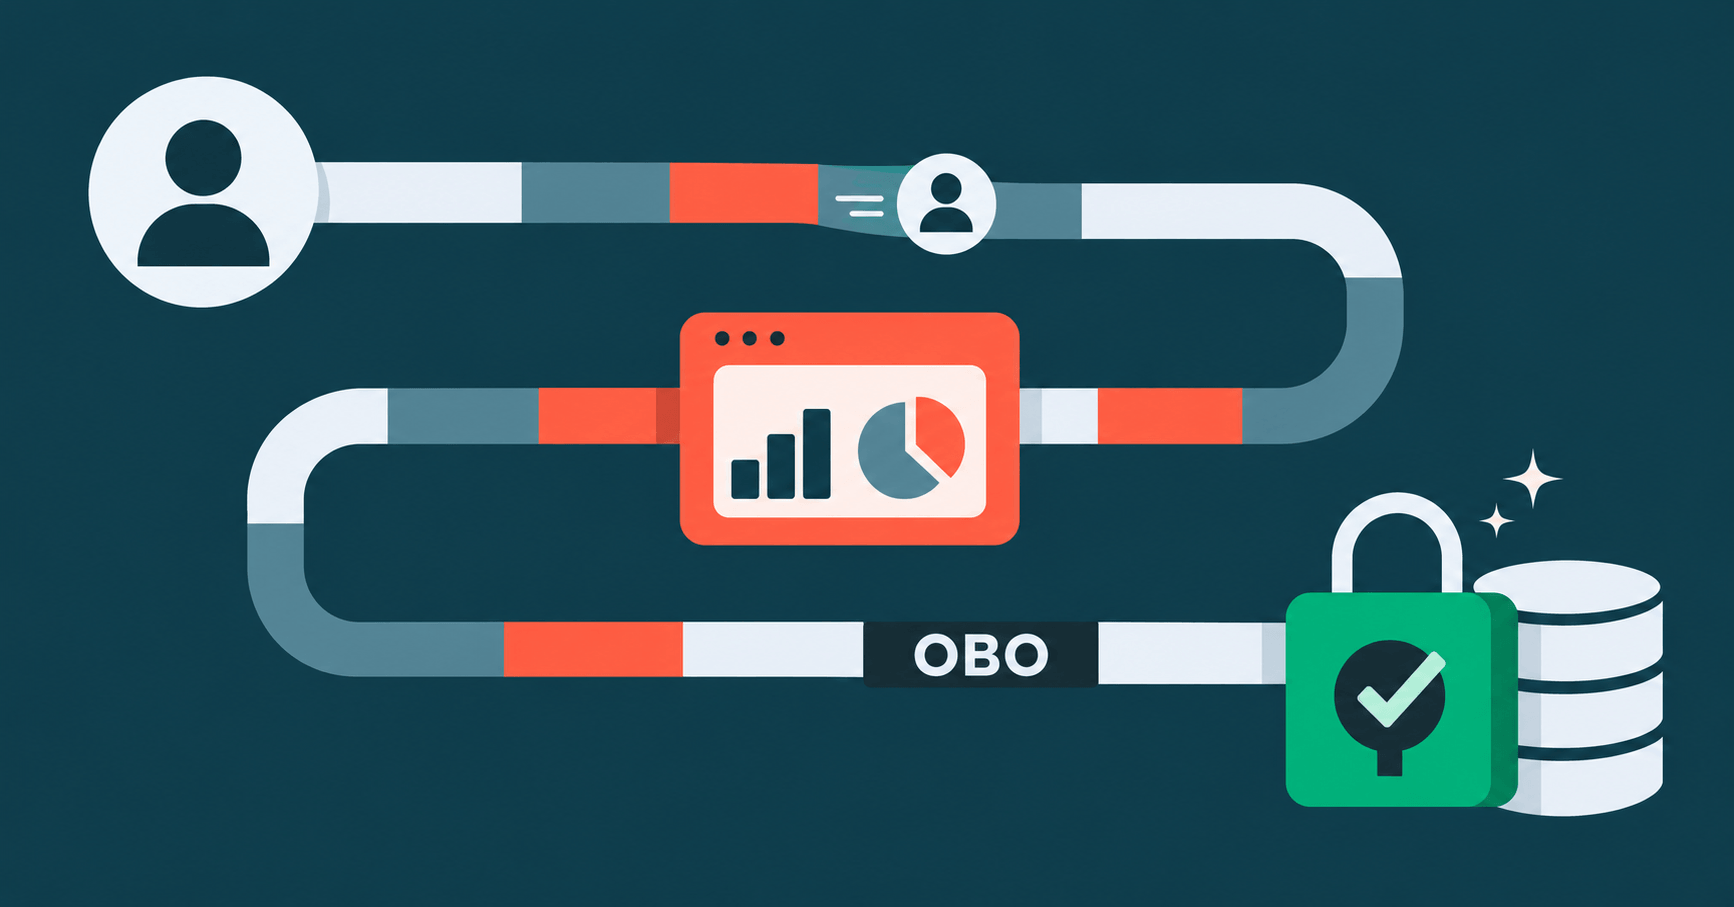
Databricks has announced the general availability of on-behalf-of-user authorization for Databricks Apps. This security feature allows developers to deploy data and AI applications, such as custom agents or interactive dashboards, that automatically run queries using the active user's identity. Instead of manually coding complex data-governance rules into an application, developers can rely on the platform to enforce existing permissions.
When an application initiates a request, Databricks forwards a short-lived access token via the x-forwarded-access-token HTTP header. The app passes this token to the Databricks SQL Connector for Python, which can be integrated into frameworks like Flask, ensuring that Unity Catalog enforces the user's specific data privileges, including row-level filters and column masks. To prevent security risks, developers are advised to use the narrowest possible API scopes. For instance, requesting the sql:restricted-query scope limits the app to read-only SQL queries, while other specific scopes like genie, ai-gateway, files, model-serving, or vector-search should only be requested when explicitly needed.
The system supports a dual-authorization model, allowing apps to separate user-governed operations from app-owned tasks. While user-scoped clients handle personalized queries, a dedicated service principal can run background tasks like writing application metrics or reading shared configurations. To maintain security, developers must design their apps to fail closed if a user token is missing. Furthermore, workspace administrators can restrict the maximum API scopes available to developers by configuring an allowlist under the development settings menu.
This is our own summary of reporting by Databricks AI